Showing posts with label cyberspace. Show all posts

Friday, January 23, 2015

Computer Vision Syndrome

mariyam | 9:11 AM | | Be the first to comment!
Explained at Vox:
A significant number of heavy computer users experience a range of symptoms that researchers group under the umbrella phrase "computer vision syndrome."...

Studies have shown that when people read from computer screens, their blink rate plummets — but this also happens when people read words from a printed page. In either case, when you blink less frequently, your eyes are much more likely to become dried out....

Eye strain is the second-most common complaint of computer vision syndrome, and can be accompanied by headaches and pain in or around the eyes... It may also lead to a related problem: difficulty focusing...

Observational studies have found that, in general, a person's level of education — and thus the amount of reading they've done over their lifetime — is positively correlated with their risk of myopia. But the direction of causation could go either way: they could have read more growing up, becoming both more educated and myopic, or for various reasons people prone to myopia could be more likely to read more...

Every twenty minutes, a person should look away from their desk for twenty seconds, and focus on something at least twenty feet away," he says. This prevents your eyes from focusing at near distances for extremely long durations, forcing them to alter their focal distance. It's also a good idea to consciously do some blinking at this sort of regular interval, in order to prevent excessive dryness. Your desk should also be set up in a way to minimize eye stress. It's recommended that your monitor be positioned 20 to 40 inches in front of your eyes, and the top of the monitor should line up with your eye level, so you're looking down about 15 degrees when you stare at the screen. 
More at the link.
Read more ...

Saturday, January 10, 2015

TYWKIWDBI sometimes eats comments - updated

mariyam | 8:01 AM | Be the first to comment!

I've received emails from readers intermittently over the years, complaining that their efforts to leave a comment on TYWKIWDBI were thwarted by some cybersnafu.  I didn't have a good explanation for them.  But this past week the problem has happened to me several times when I was writing responses to other comments, and I realized it only happened under certain circumstances...

The commenting system allows one to sign in through a variety of profiles, or to do so anonymously.  Every time I've had my comment "vaporize", it occurred when I wrote the comment first and THEN went to the pull-down menu to sign in.  The system took me to the sign-in menu (for Google in my case), and after I signed in as Minnesotastan it returned me to the commenting area - but the comment was gone.  Long, detailed comments with links in several cases, which was so frustrating I yelled at the computer.

But now I know why it happens - for me at least.  I don't know if this happens with other sign-in profiles/ operating systems/ browser combinations.  I don't think it's a peculiarity of the way I have this blog set up.  I think it's a systemic fault.

If you sign in first, this problem should not occur.  But it might be a good idea - commenting on this blog or others, that when you write a long detailed comment, copy it first before hitting the "publish" button, so that if it is eaten you can quickly try again.

I'd welcome comments from other Blogspot bloggers.

Addendum:  I received the following information from a frustrated reader in Sweden:
For the longest time now though I have not been able to post comments, and it has annoyed me to no end.

After getting a job as a whatever-do-web-stuff-person I've learned a few things, and I checked the console when trying to post and saw that I got a whole lot of cross-domain errors. This results in all my form submissions to vanish into thin air, to much despair.

What causes this is that Blogspot, which resides on .com, automatically forwards me, who is in Sweden, to .se which breaks the comment form due to different top domains. Right now I would probably have to access the site by a proxy to be able to post.
See the rest of his comment (and other useful ones) in the comments below.  At the present time I'm reluctant to try to correct this by altering TYWKIWDBI's template, but I'll consider this while awaiting other feedback and comments.
Read more ...

Thursday, January 8, 2015

New Year's greetings from TYWKIWDBI readers

mariyam | 7:20 AM | Be the first to comment!
"May all your dreams take flight in the New Year. " - Arlene


"I wish the TYWKIWDBI readers all the best for 2015" - Bert Singels


"Wishing everyone an intriguing, blessed, creative, active, curious, introspective, challenging, life-filled, love-filled, and amazing 2015." - David Crews


"I'm a baseball card collector so my blog is mostly about baseball cards.
My first post in 2008 is my favorite card." - Capewood


"Thank you to TYWKIWDBI for the great content,
and all the best to everyone for 2015!" - Leslie Hannah


"Peace unto to all in the new year!" - Jan/CascadeExposures


"Live long and prosper, everyone!"- Miss Cellania


"Do enjoy low tide walks at sunrise
and many more fantastic experiences in 2015!" - Anne in Alaska


"On behalf of RobsWebstek I wish all the readers (and the writer) of TYWKIWDBI
a creative and fruitful 2015!" - Rob From Amersfoort


"Happy New Year to TYWKIWDBI and to all of your readers!
This is Petunia, my miniature schnauzer ... she's a live wire and great fun." - Ephemeral


"Happy 2015 to MinnesotaStan and all TYWKIWDBI readers,
wherever you are!" - Bad Newspaper


"May the feeling of youth and curiosity be with us throughout 2015!!" - erin


"All the best for 2015 from The Blob,
where we don't aspire to be QI, merely I" - Bob the Scientist


"Happy New Year! May you have a delightful 2015
with lots of fun and music." - Average Jane


"Wishing a safe and happy 2015 to all." - nolandda


"Happy New Year!"  -Meredith


"I wish for everybody that 2015 may be a year full of wonder and curiosity!" - Ellen S.

"I admire the diversity of your posts and that you keep on trucking'. Best wishes." - Chris


"Wishing a happy and healthy New Year to TYWKIWDBI readers!" - Morganna

"May your year be productive and your hard work realized." --Jess
Listed in the order received, more or less.  My personal thanks to all who sent in a comment and a photo (especially the photos of yourselves - I'm always curious about the people who read this blog).

If you forgot, or missed the original invitation (which was "down" for 4-5 days because I revised it and left it in "draft" status) and would like to add your greeting to this post, just put your message and a link to your photo in the comments for this post; I'll add them on.
Read more ...

Saturday, December 27, 2014

Planning a "collective New Year's greeting card" to TYWKIWDBI readers

mariyam | 7:54 AM | Be the first to comment!
Five years ago at Christmas I set up a "collective greeting card" for the readers of this blog.  There were only about a dozen responses, but they were good ones.  I'd like to repeat the effort; it's too late for Christmas, so we'll make this a New Year's greeting.

Here are the instructions:

In the comment section to this post, give me a link to a photo (or a bit of artwork or other image) that you have in your blog, or in your Flickr photostream or in some other online storage site. Don't email me the photo - just give the link and I'll go there and copy the photo.

The picture can be of you, or your family, or your computer, or your cat, or whatever - it doesn't matter.

In the comment, with the link write a brief (25 words max) greeting, directed to the other readers and visitors (not a comment on TYWKIWDBI).

Sign with the avatar name you use in commenting here, or in your blog, or your real name if you wish. I reserve autocratic right to edit comments and trim pictures if they are too big, to limit the number if there are too many, and to vaporize anything that hints of spam or might be offensive to other readers.

I'll assemble your submissions into a collective post similiar to the one I created five years ago, and I'll post it in mid-January.

Have a go.

Addendum:  Already fifteen responses, with a couple portraits/selfies of readers, a dog photo, a cat photo, a horse, a greeting card, a scenic, one sports, a nature, a retro, and even one butterfly.  Keep 'em coming!
Read more ...

Tuesday, October 14, 2014

"Mommy, what's an Icelandic incest-blocker?"

mariyam | 8:16 AM | | | Be the first to comment!
"Well, sweetheart, if you listened to QI podcast #25, you would know that there is an app that informs Icelanders how closely related they are to a new acquaintance.  Additional details are available at the Icelandic Grapevine."
...two random Icelanders have about as much in common as second cousins, once removed, according to Dr. Kári Stefansson, CEO and co-founder of deCODE Genetics...

In early 2013, deCODE Genetics and the University of Iceland’s School of Engineering and Natural Sciences challenged the nation’s university students to design a smart phone app for the online genealogical database Íslendingabók for its 10th anniversary.

The Íslendingabók website takes its name from the Book of Icelanders, a 12th century historical text which details the Icelandic settlement. Currently, the database contains 810,000 genealogical records of “the inhabitants of Iceland, dating more than 1,200 years back.”..

...one of the novelty features of the winning ÍslendingaApp: the Sifjaspellspillir or “Incest Spoiler” alarm which alerts a user if the person she plans on going home with is a near relation. Using the app’s “new bömp technology,” users can tap their phones together and see how closely they are related. If the alarm has been activated—it’s turned off in default settings—it will either erupt with a discouraging siren, or issue a gleeful “No relation: go for it!” message...
Read more ...

Friday, October 3, 2014

A reminder that digital photos contain private information

mariyam | 9:16 AM | | Be the first to comment!
Excerpts from a Reddit thread:
Your photo contains EXIF data, which contains phone brand & model, camera serial number for some models, GPS coordinates if enabled, whether flash was used or not, focal length, etc. Some websites like Facebook, Twitter, and Imgur remove EXIF before making your photos public, but for other websites (such as Flickr, Picassa, Google+), you need to remove your EXIF by yourself before uploading. This way, the info won't be publicized along with the image.

A brother of a friend of mine was selling some kind of high end mountain bike, and took a picture of it with his iPhone. Not sure what site it was put on, but, someone got the GPS data from the photo and stole the bike a day or two later. 

[T]he concern is that most people take tons of pictures in their homes, and don't realize random strangers can find their home address from the photos. The GPS doesn't narrow down to a city, it narrows down to a few feet. That's how 4chan often tracks people down on the internet, check their blogs, look up exif from photos, order pizzas to those houses or report a shooting to get the swat team to show up or whatever.

I'm on the other side of it. I'm a professional photographer. I know how to remove and manipulate EXIF, but I usually actively add my email or other contact info to my photos so that if something gets out there and someone wants to use it for an Ad, they can get in touch with me to pay me instead of saying "I found it on the web with no info, it was orphaned so I figured I didn't have to pay anyone."
Read more ...

Monday, September 29, 2014

"Shellshock" - a scary new computer bug

mariyam | 9:19 AM | | Be the first to comment!
From the BBC:
The flaw has been found in a software component known as Bash, which is a part of many Linux systems as well as Apple's Mac operating system. The bug, dubbed Shellshock, can be used to remotely take control of almost any system using Bash, researchers said...

"Whereas something like Heartbleed was all about sniffing what was going on, this was about giving you direct access to the system," Prof Alan Woodward, a security researcher from the University of Surrey, told the BBC.

"The door's wide open."

Some 500,000 machines worldwide were thought to have been vulnerable to Heartbleed. But early estimates, which experts said were conservative, suggest that Shellshock could hit at least 500 million machines...

"Using this vulnerability, attackers can potentially take over the operating system, access confidential information, make changes, et cetera," said Tod Beardsley, a Rapid7 engineer...

For general home users worried about security, Prof Woodward suggested simply keeping an eye on manufacturer websites for updates - particularly for hardware such as broadband routers.
More at the link. I would welcome comments from some of the informed readers of this blog.
Read more ...

Saturday, August 30, 2014

Richard Feynman's lectures on physics are now online

mariyam | 8:02 AM | | | Be the first to comment!

As reported by Open Culture:
Last fall, we let you know that Caltech and The Feynman Lectures Website joined forces to create an online edition of The Feynman Lectures on Physics. They started with Volume 1. And now they’ve followed up with Volume 2 and Volume 3, making the collection complete...

The new online edition makes The Feynman Lectures on Physics available in HTML5. The text “has been designed for ease of reading on devices of any size or shape,” and you can zoom into text, figures and equations without degradation. 
More at the link.  The image is my screencap of part of one of the pages.
Read more ...

Monday, August 25, 2014

"Some quality family bonding time right here..."

mariyam | 7:35 AM | | Be the first to comment!


An instagram tweeted by a member of my cousin's family, who was in the process of packing to head off to college and taking some last pix of family she would leave behind.

It's sort of meta for me to now post it in the blog for them to see.  And now I'll email it to my wife.  My 95-year-old mother is forever amazed by "this modern world."
Read more ...

Thursday, August 21, 2014

Millions more personal records stolen

mariyam | 7:48 AM | | | Be the first to comment!
Community Health Systems, which operates 206 hospitals across the United States, announced on Monday that hackers recently broke into its computers and stole data on 4.5 million patients.

Hackers have gained access to their names, Social Security numbers, physical addresses, birthdays and telephone numbers.

Anyone who received treatment from a network-owned hospital in the last five years -- or was merely referred there by an outside doctor -- is affected.

The large data breach puts these people at heightened risk of identity fraud. That allows criminals open bank accounts and credit cards on their behalf, take out loans and ruin personal credit history.
It never ends...
Read more ...

Did someone hack Google Translate?

mariyam | 7:23 AM | | Be the first to comment!
From Krebs on Security:
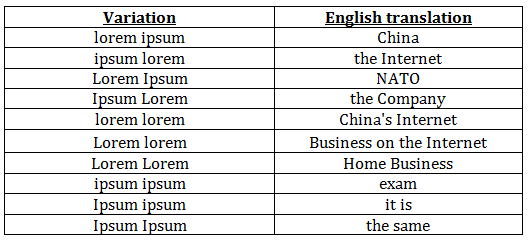
It all started a few months back when I received a note from Lance James, head of cyber intelligence at Deloitte. James pinged me to share something discovered by FireEye researcher Michael Shoukry and another researcher who wished to be identified only as “Kraeh3n.” They noticed a bizarre pattern in Google Translate: When one typed “lorem ipsum” into Google Translate, the default results (with the system auto-detecting Latin as the language) returned a single word: “China.”

Capitalizing the first letter of each word changed the output to “NATO” — the acronym for the North Atlantic Treaty Organization. Reversing the words in both lower- and uppercase produced “The Internet” and “The Company” (the “Company” with a capital “C” has long been a code word for the U.S. Central Intelligence Agency). Repeating and rearranging the word pair with a mix of capitalization generated even stranger results. For example, “lorem ipsum ipsum ipsum Lorem” generated the phrase “China is very very sexy.”
Until very recently, the words on the left were transformed to the words on the right using Google Translate.

Kraeh3n said she discovered the strange behavior while proofreading a document for a colleague, a document that had the standard lorem ipsum placeholder text. When she began typing “l-o-r..e..” and saw “China” as the result, she knew something was strange.
More at the link.
Read more ...

Monday, August 4, 2014

Google Maps no longer offers "search nearby" function

mariyam | 8:30 AM | Be the first to comment!
I recently tried to find a certain type of business near a certain location and discovered that I could no longer use Google Maps for that purpose.  A quick search retrieved this confirmatory article:
Ironically, the [updated] maps appear to have become less customer friendly in one important regard: One of the features that Google maps took away on the left side was the "Search nearby" function. That has many users complaining.

The issue is that instead of showing users common places such as restaurants, cafes, pharmacies or post offices, the default Google Maps appears to be focused on people who are completely unfamiliar with the area. Google Maps now wants to show us photos of nearby tourist attractions...

Earlier today, I tried to find a coffee place to meet with a source. I typed in an address in the general area where I planned to go, figuring I'd hit the "search nearby" function afterward as I normally do. No such button was anywhere to be found. ..

Apparently, I'm not the only one who's frustrated with the "search nearby" function being taken away. SlashDot posted complaints about it about a month ago and more than 400 people posted comments on it in the Google Product Forum.

Google community manager Daniel posted a reply to those comments Feb. 20, saying there are two ways to do a nearby search now... [continued at the link]
Read more ...
Twitter Delicious Facebook Digg Stumbleupon Favorites More

Search

Pages

Powered by Blogger.